The boom of the global online entertainment market in recent years has triggered a chain reaction from international financial and gaming regulatory authorities. Entering 2026, the term “grey market” is gradually being eliminated as legal institutions shift from passive oversight mechanisms to active technical enforcement.
Monitoring regulatory tightening trends in the iGaming industry in 2026 not only helps operators adapt to legal regulations, but also serves as a benchmark for users to evaluate the credibility and safety of digital platforms.
Background of global legal framework tightening in 2026
According to the latest updates from Hitclub, 2026 is witnessing unprecedentedly rigorous cross-border cooperation between gambling regulators and international anti-money laundering organizations.
AMLA legal framework in Europe
The European Anti-Money Laundering Authority (AMLA) officially became operational with synchronized regulations across all 27 member states. The core change in these regulatory tightening trends is the elimination of overlaps between domestic laws, establishing a unified compliance set (Single Rulebook). Platforms with large cross-border transaction volumes are subject to direct supervision and real-time transaction data sharing to the EU’s centralized reporting interface.
Tax imposition and stake cap tightening at the UKGC (United Kingdom)
The United Kingdom Gambling Commission (UKGC) simultaneously applied two aggressive measures: raising the Remote Gaming Duty to 40% and officially codifying Stake Caps for online games.
Specifically, maximum stakes are limited to £2 per spin for players aged 18–24 and £5 per spin for players aged 25 and older. At the same time, Frictionless Financial Risk Checks are automatically deployed based on credit data.
Tightening control over cryptocurrency flows (Crypto Assets)
With the full implementation of the Markets in Crypto-Assets (MiCA) regulation, platforms accepting crypto asset payments are required to enforce the Travel Rule. All deposit/withdrawal transactions using stablecoins or cryptocurrencies reaching designated thresholds must clearly identify source and destination wallet identities through licensed Crypto Asset Service Providers (CASPs).
Mandatory RegTech technical pillars in operations
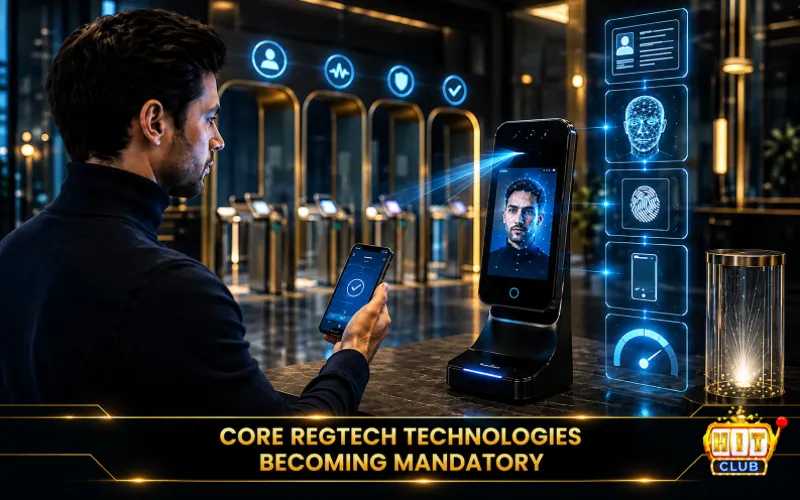
To comply with new sanctions resulting from regulatory tightening trends, the iGaming industry is witnessing a strong shift toward applying Regulatory Technology (RegTech). Compliance is no longer just paper-based procedures, but is integrated directly into software architecture.
| Standard | Technical Solutions & Integrated Infrastructure |
| Tiered eKYC | OCR + AI Liveness Detection (Real face verification) |
| PEP & Sanctions database screening (Blacklists) | |
| AML Control | Device Fingerprinting |
| Risk Scoring (Transaction behavior risk scoring) | |
| Responsible Gaming | Syncing Self-Exclusion data |
| Reality Checks & Playtime limit alerts |
Tiered eKYC process (Tiered Identity Verification)
Electronic identity verification is no longer limited to simply uploading identity documents. The standardized eKYC process in 2026 is divided into 3 tiers:
- Basic tier: Verifying name, age, and IP address upon account registration.
- Intermediate tier: Using OCR technology to scan documents combined with AI Liveness Detection (facial liveness verification) before processing deposit/withdrawal transactions.
- Advanced tier (Enhanced Due Diligence): Requiring Source of Funds proof for accounts with high transaction limits or detected risk indicators.
Transaction risk control (AML & Risk Scoring)
Responding to the industry trend of tightening regulations in 2026, instead of manual checks, RegTech systems apply a Risk-Based Approach model using machine learning algorithms. The system automatically scans for anomalies such as:
- Continuous deposits and withdrawals with extremely low betting participation rates (a sign of money laundering).
- A single account logging in from multiple different devices within a short timeframe or constantly changing IP ranges (using invalid VPNs/Proxies).
- Identifying duplicate Device Fingerprints to detect fake account networks.
User protection system (Responsible Gaming Tools)
According to new regulations under regulatory tightening trends from the MGA and UKGC, Responsible Gaming tools must be activated by default. Users have the right to set Deposit Limits and Loss Limits on a daily/weekly/monthly basis. When an account hits a self-imposed threshold or requests Self-Exclusion, the system must be capable of freezing access immediately without reversal during the configured period.
Cybersecurity standards and independent algorithm audits
Information security and game transparency are prerequisites for an iGaming platform to maintain legal operation amidst regulatory tightening trends.
Data encryption and Zero-Trust Architecture
All data transmitted between users and the system must be encrypted using the TLS 1.3 protocol combined with the AES-256-GCM algorithm. The information security management framework must strictly comply with ISO/IEC 27001 certification. Additionally, technical organizations adopt a Zero-Trust Architecture (Trust no one, always verify) to prevent data
>>Read more: iGaming 2026 Trends: The Shift in Technical Infrastructure
Random number generator auditing (RNG & RTP Audit)
In line with regulatory tightening trends, fairness in gaming cannot rely solely on publisher commitments. Pseudo-Random Number Generator (PRNG) algorithms and Return to Player (RTP) rates are required to be independently audited and certified by reputable international testing labs such as GLI (Gaming Laboratories International) or iTech Labs. The audited algorithm source code is sealed, and any configuration changes made without auditor approval are considered severe violations.